KIISC
MOBISEC 2026
The 10th KIISC International Conference on Mobile Internet Security
Date: December 15–17, 2026
Venue: Splendor Hotel, Taichung, Taiwan
Collaborators
Organized & Supported By
KIISC
Mobile Internet SecurityLocation
Conference Venue
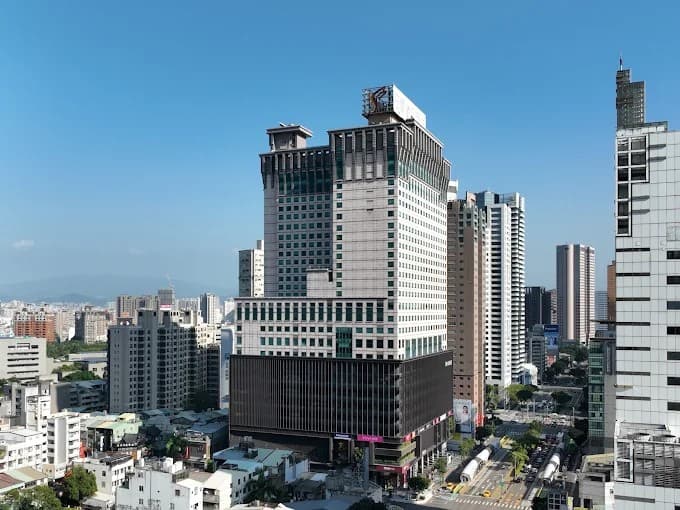
Splendor Hotel
No. 1049, Jianxing Rd., West District, Taichung City 403, Taiwan
About the Venue
Splendor Hotel Taichung is a premier conference hotel in the heart of Taichung, Taiwan, located at the intersection of Taiwan Blvd and Jianxing Rd, offering modern meeting facilities alongside easy access to the city's cultural and business districts.
Visit Official WebsiteGetting There
Located in central Taichung at Taiwan Blvd & Jianxing Rd, within easy reach of Taichung HSR Station by shuttle or taxi, and close to Taichung Chiang Kai-Shek Memorial Park and the National Museum of Natural Science. Taichung International Airport (RMQ) is approximately 30 minutes away by car.
Submissions
Call for Papers
MobiSec 2026, the 10th KIISC International Conference on Mobile Internet Security, invites researchers, practitioners, and students to submit original research papers that advance the field of mobile internet security.
Regular Paper
Important Dates
Paper Submission Deadline
October 3, 2026 (KST/JST)
Acceptance Notification
October 28, 2026 (KST/JST)
Final Version Deadline
November 8, 2026 (KST/JST)
Requirements
Anonymous submission: No author names, affiliations, or self-references
PDF format: EasyChair LaTeX or Word template
Page length: 5–20 pages in EasyChair style
Original work: Must not overlap with published work
Poster Paper
Important Dates
Submission Deadline
October 23, 2026 (KST/JST)
Acceptance Notification
October 31, 2026 (KST/JST)
Final Version
November 8, 2026 (KST/JST)
Requirements
Submission format: Single PDF with poster abstract and poster draft
Poster abstract: Max 2 pages, not anonymized, EasyChair template
Poster draft: 32×40 inches (scalable to letter size)
Select "MOBISEC 2026 - Poster Track" during submission
General Requirements
All papers must be original and not simultaneously submitted to another journal or conference. The contributions to MOBISEC 2026 must be submitted to the conference submission system: EasyChair
For detailed submission guidelines, file formats, and requirements for both Regular Papers and Poster Papers, visit the Author Instructions page.
Author InstructionsProceedings & Post Publications
All accepted papers will be made available to participants in the preliminary online proceedings (non-official publication) during the conference.
Online proceedings
All accepted papers are published in the conference's online proceedings (non-official): participants receive access for reading and citation during and after the event.
Springer CCIS post-conference proceedings
Following our tradition, a selected set of high-quality papers presented at MobiSec 2026 will be invited for publication in the Springer Communications in Computer and Information Science (CCIS) series (indexed by Scopus), after appropriate revision and expansion.
Topics of Interest
- Security for 5G/6G and Next-Generation Mobile Networks
- Quantum Security
- Mobile, Wireless, and Cellular System Security
- Network/Edge/Cloud Security and Infrastructure Protection
- Data Security and Privacy in Edge and Distributed Environments
- (Post-Quantum) Cryptography, Lightweight/Advanced Encryption, and Side-Channel Countermeasures
- Security for IoT and Cyber-Physical Systems
- Embedded Systems and Hardware Security
- Trusted Execution Environments and Trustworthy Computing
- Security for AI Systems and Applications of AI in Security (e.g., AI-Driven Threat Detection)
- Digital Forensics and Malware Analysis in Mobile Ecosystems
- Secure Access Control, Authentication, and Authorization
- Secure Protocol Design and Real-World Protocol Analysis
- Blockchain and Distributed Ledger Security
- Supply Chain Security and Digital Platform Ecosystem Resilience
- Automated Tools for Software/Binary Vulnerability Analysis
- Operating System, Storage, and File System Security
- Web and Application Security
- HCI Security and Privacy (e.g., for Wearables and Smart Devices)
- Security for Unmanned Systems (Vehicles, Drones, Ships)
- Denial-of-Service Attacks and Botnet Defense
- Exploit Techniques, Vulnerability Research, and Practical Cryptanalysis
- Privacy-Preserving Technologies (e.g., Anonymity, Anti-Censorship Tools)
- Security Policy, Management, and Governance Models
- Safety and Security Issues in Digital Transformation and Industry 4.0/5.0 Platforms
- Emerging Trends and Challenges in Mobile Internet and Application Security
- Case Studies and Practical Security Applications in Real-World Environments
- Others and Emerging New Topics in Mobile Internet Security
Ready to Submit?
Join leading researchers and practitioners in advancing Mobile Internet Security research.
Questions about submissions? Contact us at cyberchair.mobisec@gmail.com